
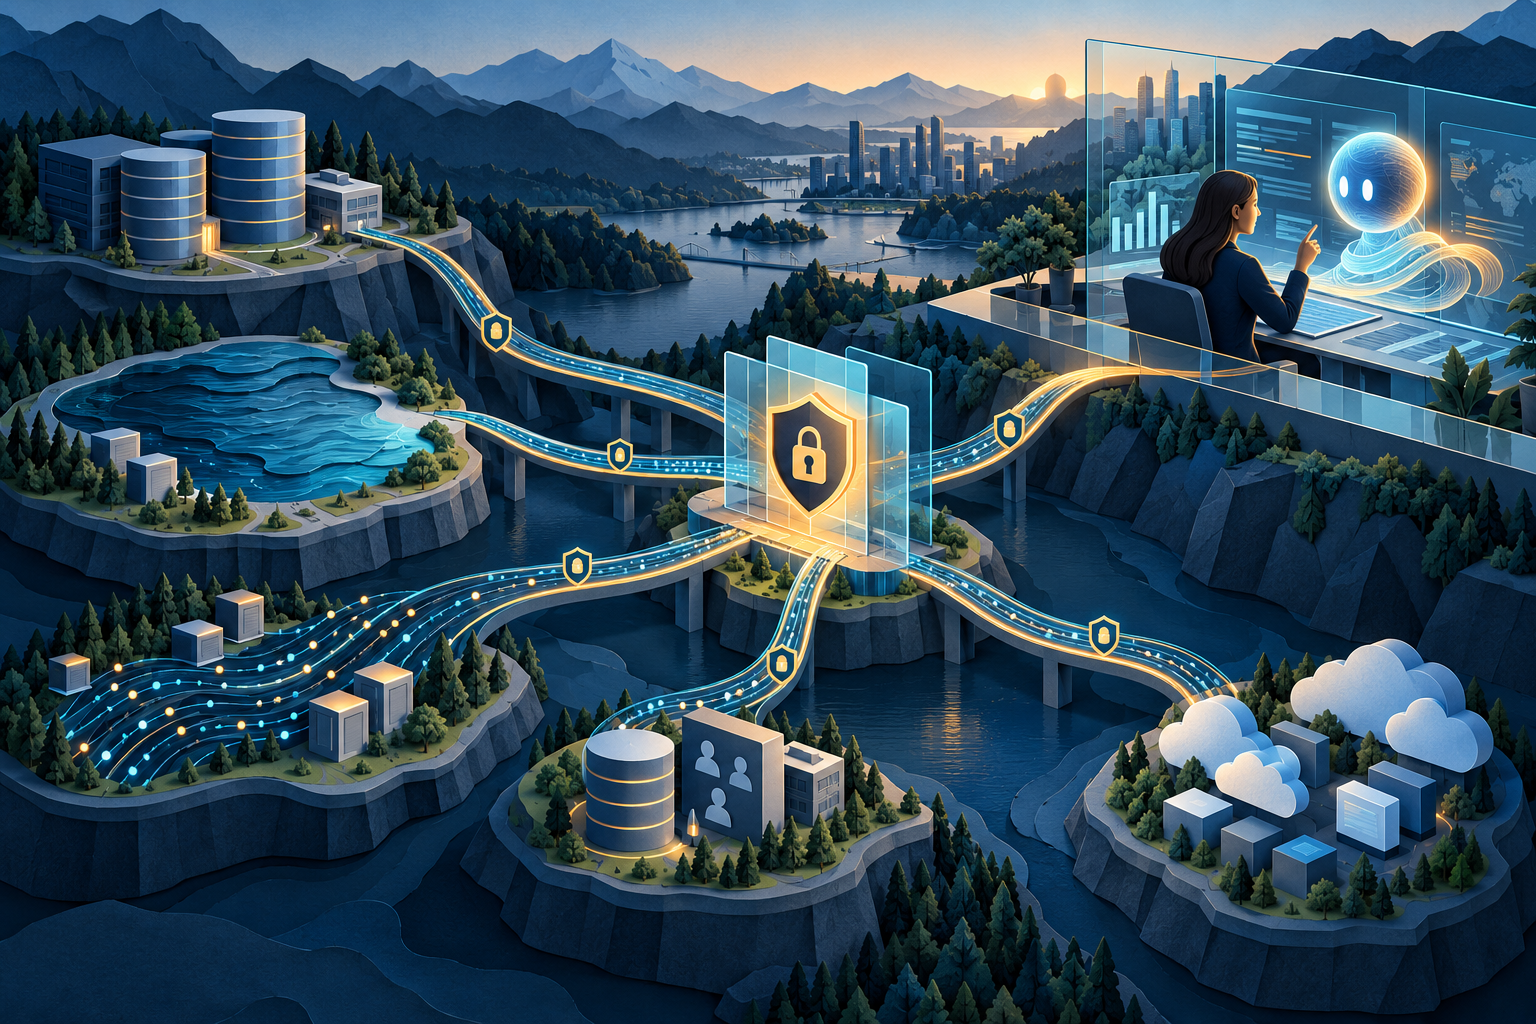
Enterprise data rarely lives in one place. Historical files sit in object storage, operational records remain in relational systems, telemetry arrives through streams, and customer activity is held inside SaaS applications. A new AI assistant can make that fragmentation visible immediately: a simple business question may require several query languages, identities, and access paths.
The traditional answer is to copy everything into a central platform. Centralization remains valuable for governed analytics, but it is not always the fastest or safest route for every agent question. Federated access offers another pattern: keep data in the systems that own it and expose controlled capabilities through a common tool interface.
Three useful access patterns
A catalog-first pattern begins with metadata. The agent discovers approved datasets, ownership, sensitivity, freshness, and access methods before selecting a tool. This works well when governance and discoverability are the main challenge.
A direct-source pattern exposes narrowly scoped tools close to each system. A warehouse tool can run read-only SQL; a streaming tool can retrieve an aggregate; a CRM tool can return an authorized customer view. This minimizes copying and preserves source-specific controls, but it requires consistent tool contracts and identity handling.
A hybrid pattern combines curated central data for common questions with federated calls for current or specialized facts. It often gives the best balance: repeatable analytics stay optimized, while one-off questions do not create permanent ingestion pipelines.
The gateway is a policy boundary
An agent gateway can present APIs, functions, and MCP servers through one discovery and invocation surface. Treat that gateway as a security control, not merely a protocol translator. It should authenticate the calling agent and user, authorize each tool, validate arguments, constrain output, record an audit trail, and enforce rate and spend limits.
Tools should describe business capabilities rather than raw infrastructure. “Get approved subscriber-retention metrics” is safer and easier to govern than unrestricted database access. Return structured results with lineage, freshness, and error metadata so the agent can reason about evidence quality.
Preserve user context
Agent identity must not erase the permissions of the person who initiated the task. Carry user, tenant, purpose, and consent context through the gateway. Apply least privilege at every source. For sensitive data, consider row- and column-level controls, masking, and purpose-based policies.
Do not put secrets or excessive data into tool descriptions. Limit discovery to capabilities the caller may actually use. A tool catalog can leak as much architectural information as an API inventory if exposed broadly.
Design for partial answers
Federated systems fail independently. One source may be unavailable, slow, or denied while others respond. The agent should identify missing evidence instead of fabricating a complete answer. Establish timeouts, circuit breakers, per-source confidence, and a clear rule for when human review is required.
Cache stable metadata and safe aggregates, but respect source freshness and revocation. Observability should connect the user question to tool selection, source calls, policy decisions, latency, returned records, and the final response.
Start with a bounded question
Choose a cross-system question with measurable value and known owners. Build a small set of read-only tools, compare answers with an existing analyst process, and evaluate correctness, policy enforcement, latency, and cost. Add write actions only after read paths and audit controls are dependable.
The takeaway
Federated agent access is not a shortcut around data governance. It is a way to apply governance at the point of use while avoiding unnecessary copies. Success depends on catalogs, narrow tools, identity propagation, source-aware failure handling, and an auditable gateway.
Sources
- AWS: Federated data access patterns for AI agents
- AWS documentation: AgentCore Gateway core concepts
- AWS documentation: Using an AgentCore Gateway
Build it with Cogniquaint experts
Cogniquaint’s data and AI experts can work alongside your teams to map distributed sources, design secure MCP and API tools, implement gateway policies, and validate a federated access pilot against real business questions.
Work with Cogniquaint
Ready to elevate your operations with AI-powered insights?
Get in touch with us to build your next intelligent solution.